
Senior in-house counsel share candid views on AI tools, governance frameworks and the urgent need for privacy law reform in Canada
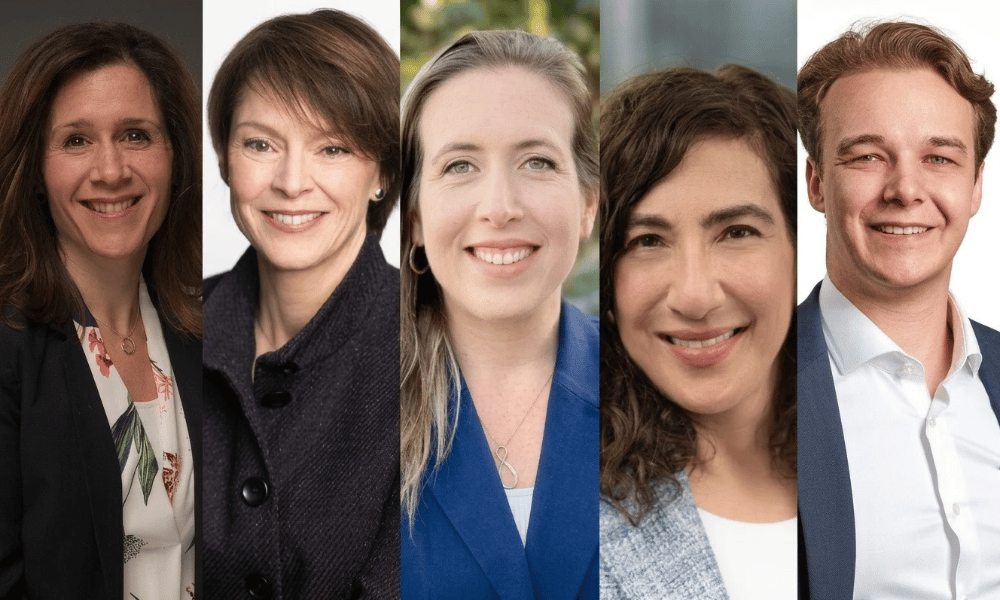
Canada's healthcare system is undergoing rapid digital transformation, and the legal departments that govern it are navigating uncharted territory. From lean Canadian subsidiaries queued at the back of global AI deployment schedules to community hospitals running week-long clinical downtime simulations, the pressure to build governance frameworks that work in practice – not just on paper – has never been more acute. At the third Canadian Lawyer Leaders Network roundtable, senior in-house legal leaders from across the health sciences sector gathered to discuss AI governance, cybersecurity preparedness, and regulatory gaps that are constraining care transformation at a time when healthcare systems can least afford it.
PARTICIPANTS
|
Name |
Title |
Organisation |
|
Nicole Vaz |
Senior Vice President, General Counsel & Chief Compliance and Privacy Officer |
Trillium Health Partners |
|
Anne Mayrand |
Organon Canada |
|
|
Luciana Andrade |
Head of Legal, Canada |
Edwards Lifesciences |
|
Rosie Kogan |
Medcan |
|
|
Vincent Rocheleau |
dentalcorp Health Services Ltd. |
Topic 1: Deployment queues, data sources and the case for tiered governance
Q (Tim Wilbur): What is the most significant AI-related legal or governance issue currently on your desk?
Nicole Vaz
We know AI is out there. Public hospitals are catching up. At THP, we are committed to bold, innovative approaches that harness the power of digital technology and AI to meet the rapidly changing needs of our community. The most significant issue on my desk is establishing the governance framework for legal and privacy support that enables us to move more efficiently beyond exploring AI and into deployment – creating the reassessment cycles that enable quick deployment, while also allowing us to monitor, modify, and redeploy as needed, so we aren't spending undue time at the outset.
Anne Mayrand
In our company, AI governance is established globally. However, having a governance framework is one thing; becoming truly proficient in both the technology itself and the way the framework operates in practice is another. Like many organizations, we are still on that learning journey. Are we competitive in our use of AI when launching pharmaceutical products? It's too early for me to say with confidence.
Luciana Andrade
As a Canadian subsidiary within a smaller part of the organization, we are sometimes excluded from tool deployments. As eager as I am to get access to these tools quickly, and I know that they can help enormously, it can take time to be part of the deployment.
Topic 2: The source problem: what legal AI tools can and cannot do in a Canadian healthcare context
Q (Tim Wilbur): What legal AI tools are you using, and what have you learned about their limitations?
Luciana Andrade
I found GC AI to be very helpful – especially for those odd questions you receive as head of legal, where you have no background and don't know where to start. What I found interesting is that it provided me with stricter guidance than Copilot on the same question. My working theory was that Copilot has access to our internal corporate policies and risk profile, calibrating its guidance to our specific context.
Rosie Kogan
We ran a comparison between two tools using the same prompts for an insured and an uninsured services question. The response from the first tool, Legal AI, was extremely permissive compared to the other results from an enterprise AI tool. The working theory we have is that, because private pay for healthcare is commonplace in the American regulatory system compared to the Canadian system, the result may have been influenced by a different regulatory regime than the one the Legal AI tool was trained on, which we operate under. That is very relevant in our healthcare context.
Vincent Rocheleau
We are using Harvey. We also tested Protégé, Legora, Jurist, and Vincent. We found that it is imperative for any AI that provides support with drafting or research to have access to case law behind paywalls. If the AI does not have access to these databases, it is more likely to provide an incorrect or unhelpful answer. In any event, legal team members must always review what any AI produces.
Nicole Vaz
We aren’t currently using AI tools specific to legal or privacy, but we are exploring the development of in-house tools to maximize efficacy and reliability.
Topic 3: From gatekeeper to embedded infrastructure: legal's evolving role in AI governance
Q (Tim Wilbur): How is legal's role in AI governance changing, and what does effective involvement look like?
Nicole Vaz
What we're trying to move away from is focused issue spotting and discrete, siloed legal issues. We're trying to step in at the design phase to understand the materiality threshold that this AI initiative will create, so we can start driving risk-based governance. Everything's unprecedented – we're building the plane while we're flying it.
By introducing AI into the organization, we are, by definition, creating increased exposure. We need to do it. But the relationship between AI and cybersecurity is not always symbiotic. While AI can strengthen cybersecurity, it also has the potential to undermine it.
Our community expects that the appropriate regulated health professional oversees the diagnosis and treatment being provided. Ensuring we have a clear understanding of professional accountabilities will be an issue to navigate well.
Rosie Kogan
Legal built the governance framework and is a co-owner of the process along with the data and AI enablement function, so we’re in a unique position to be part of those conversations early on. We’re also the subject-matter experts who participate in the process by identifying which guardrails are needed, where, and how to put them into practice.
The place where we add the greatest value is in developing practical, achievable guardrails. We are also able to bring together the different stakeholders and subject matter experts from security, clinical and the business. Our role is to help ensure they are all working from a common understanding of what we’re looking to do, what information is involved, how an output may be used, who may be affected and what could happen if the output is wrong. That is very much the role legal plays in other initiatives, and it’s now about applying it to AI.
Anne Mayrand
I'm asking myself: are we considering asking our suppliers whether they use AI? Are we proactively auditing whether third-party vendors – particularly those supporting advertising to healthcare professionals – are using AI, and updating contracts accordingly? In AI governance, I think we're at the SOP stage, not the effective training stage. Speaking for myself, I still do not know what I don't know.
Nicole Vaz
Right now, our role is very much gatekeeping. Within THP’s AI governance model, we are working to embed standard legal and privacy guardrails that empower teams to operate more autonomously. By being part of the design, our gatekeeping role evolves. We put this together, and now we're actually part of the infrastructure, part of the skeleton that the organization is using.
Topic 4: Beyond breach response: cybersecurity preparedness in a healthcare context
Q (Tim Wilbur): How is your organization approaching cybersecurity preparedness, and how has the role of legal evolved?
Nicole Vaz
What we know is that, sitting around a table, issue-spotting will not do justice to how it will actually feel to lose some or all of your systems, and it is important to ensure that certain decisions and protocols are clear, concise, and usable under very stressful and time-sensitive circumstances before an incident occurs. Vendor security should also become a distinct workstream in contract negotiations. Systems will be interdependent, and you will only be as strong as your weakest partner.
Luciana Andrade
Despite having too many policies, the business still came to Legal for advice on them. So it kind of defeats the purpose of a policy: alignment. Edwards tries to check whether people understand what they need to do by openly releasing a draft policy for challenge and questions, then incorporating feedback into a second version. I thought that was a very interesting new approach to building policy, and it fits very well with AI because the use cases and the need are so vast.
Anne Mayrand
Over the last few years, a number of pharmaceutical companies have been affected, directly or indirectly, by data security incidents involving third-party vendors supporting patient support programs. These events, together with other developments that can increase external interest in a company, have led to more frequent attempts to obtain information from employees through social engineering and other means. As a result, protecting sensitive information requires not only robust technical safeguards and security measures, but also a strong first line of defence: informed, vigilant employees who understand how to recognize and respond to potential threats.
Topic 5: PHIPA, PIPEDA and the case for regulatory reform
Q (Tim Wilbur): What regulatory and privacy frameworks create the most uncertainty for your organization, and what changes would you like to see?
Nicole Vaz
When we look at AI in the public healthcare sector – we're living in unprecedented, financially constrained times resulting from population growth and more complex illnesses – we see that our systems, as they are designed and used now, will not meet the needs of our community. We all need to transform how we deliver care through AI initiatives. The privacy laws, which have not evolved with digital and AI systems, constrain us in so many ways from advancing patient care.
Ontario hospitals exist as siloed legal entities – a patient seen at one hospital may not exist in another hospital's system down the road. That makes no sense in 2026.
The IPC's recent guidelines on de-identification of personal health information exceed 135 pages and are practically unachievable in most instances. By contrast, British Columbia has adopted internationally recognized, principles-based de-identification standards.
It’s more than a question of what I would like to see. There is an urgent need to modernize privacy laws and guidelines to enable seamless patient care across the province. To ensure that personal health information is readily accessible to health care providers within a patient’s circle of care, no matter where the patient is seen in the province. This is what patients are expecting, and this is what they deserve.
Rosie Kogan
As AI becomes more embedded in healthcare, I think one of the biggest questions will be how human judgment and AI-supported decision-making are meant to work together in practice, and what meaningful oversight looks like. We tend to treat human involvement as the solution, but I think the reality is more complicated than that. Automation bias is real. At the same time, there may be situations where the technology achieves a more accurate result than a clinician.
Anne Mayrand
I would like to have either the provinces align on key standards or the federal government adopt the same standard, which should also more or less align with international standards. What Yoshua Bengio has been saying about the systemic risks of AI development – the news over the last few weeks – is concerning, and that goes beyond my role within Organon Canada.
Vincent Rocheleau
PIPEDA’s potential reform creates the most uncertainty. I fear that if the overhaul goes through, we may see other provinces follow suit quickly. Ensuring adequate compliance may be difficult, as businesses won’t be able to apply the highest standards in multiple jurisdictions. Some provinces already require a bespoke approach.